This project is a network monitoring and intrusion detection setup designed to inspect traffic between the internet and a web server hosted in a DMZ. The goal is to perform deep inspection on inbound traffic by decrypting HTTPS and routing the resulting HTTP traffic through a Suricata inline IPS.
Network architecture
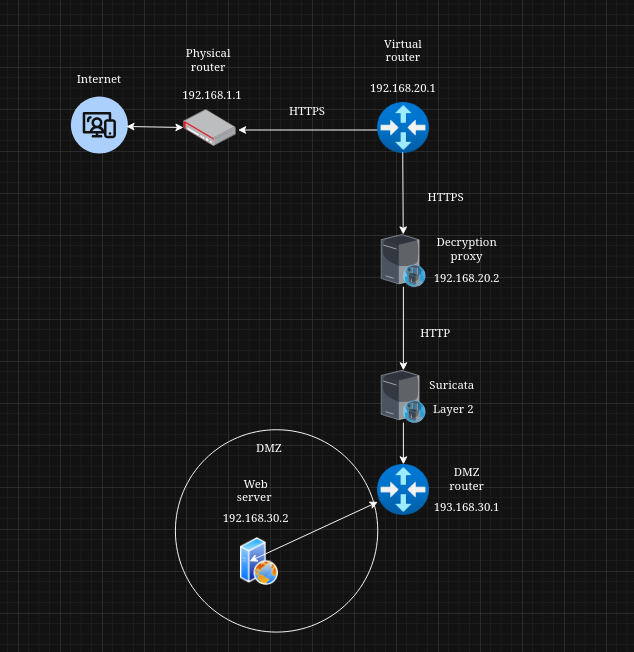
Traffic from the internet reaches a physical router, which forwards all packets destined for my public domain into a virtual OPNsense router. This virtual router is isolated and cannot access any internal networks. It forwards HTTPS traffic to a TLS decryption proxy. Once decrypted into HTTP, the traffic passes through a Suricata layer 2 inline IPS before reaching a final router that leads into the DMZ containing the web server.
TLS decryption proxy
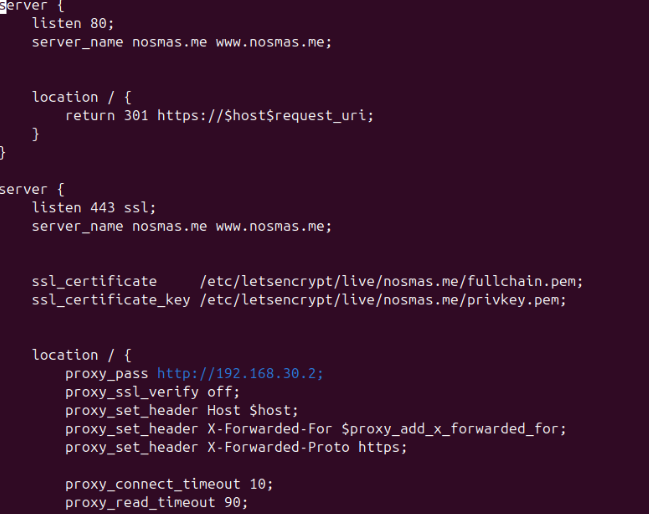
The TLS decryption proxy terminates inbound HTTPS requests, rewrites headers, and forwards the resulting HTTP traffic to Suricata. Below is the configuration used for decryption and forwarding.
Suricata inline inspection
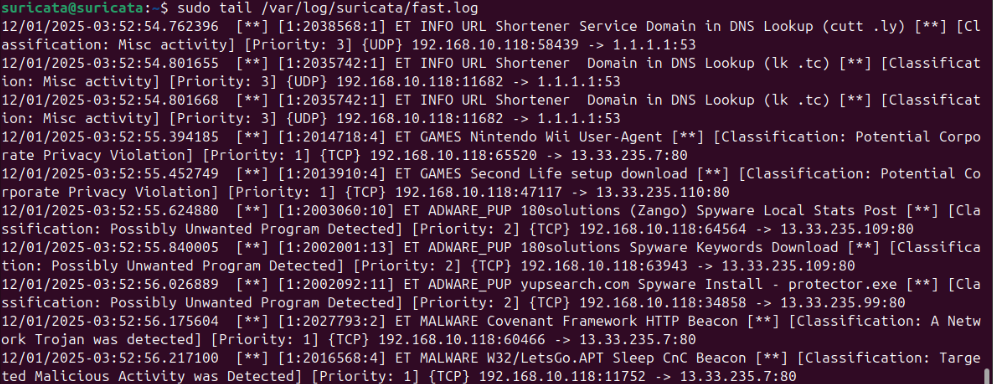
Suricata operates in inline mode, receiving plain HTTP traffic from the proxy. Using the test suite from testmynids.org, all signature tests correctly triggered alerts in Suricata. This confirms that decrypted traffic is being inspected end to end and that IPS functionality is active.
Limitation
At this stage, only inbound traffic is decrypted and inspected. Outbound HTTPS from the web server is not visible to Suricata, which introduces a blind spot. If the server were compromised and attempted to establish an HTTPS C2 connection, this setup would not detect it.
What came next
The plan here was a second decryption proxy for outbound traffic. Instead, the whole design got rebuilt in part 2, Overhaul: the lab is split into isolated zones, the site is published through an outbound-only tunnel, and logs flow into a push-only SOC. The web server now has no outbound access at all, which closes the C2 blind spot described above.